#e4mXplains: What the global PHP security crisis means for digital advertising
As millions of attempted cyberattacks send businesses scrambling to secure websites, questions are being raised about publisher infra, advertising continuity & dependencies of AI-powered economy
 by
Published: Oct 24, 2026 9:14 AM | 7 min read
 Follow Us
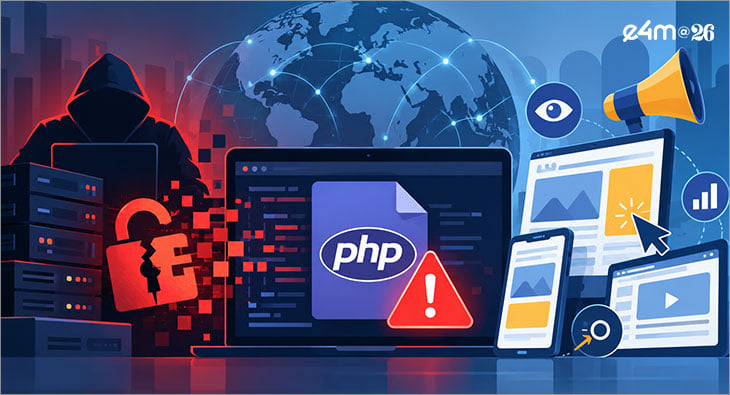

- On October 21, two critical vulnerabilities in PHP, a widely used programming language for websites, prompted a global rush to implement security updates, leading to millions of attempted cyberattacks within hours.
- Microsoft CEO Satya Nadella noted the unprecedented response from IT professionals, highlighting the urgency to secure existing internet infrastructure amidst ongoing investments in artificial intelligence by tech companies.
- The vulnerabilities, discovered with AI assistance, could potentially disrupt digital advertising operations, affecting website availability and data security, although no widespread damage has been confirmed as of October 23.
- The incident raises questions about accountability in digital advertising, as multiple intermediaries are involved, and emphasizes the need for robust security measures to protect the interconnected systems that underpin the industry.
As if the technology industry needed another headache.
Between quarterly earnings dominated by ballooning artificial intelligence investments, nervous investors scrutinising returns, and increasingly expensive infrastructure ambitions, Big Tech, and the poor little world's richest people who run them, were already having a rather stressful week. Then came a reminder that building the internet of tomorrow is one thing. Keeping yesterday's internet secure is quite another.
On October 21, two critical vulnerabilities in PHP, a programming language operating behind millions of websites, triggered an international scramble to install security updates.
Within hours, attempted cyberattacks had reportedly climbed into the millions. Governments and businesses temporarily suspended services, while security teams raced to protect infrastructure that had, until recently, been going about its business without much attention.
Microsoft CEO Satya Nadella acknowledged the extraordinary response, saying he had not seen anything comparable in a long time, with IT professionals working through the night.
For an industry preoccupied with how AI will transform everything, it was a reminder that everything includes the systems everyone already depends on.
For digital advertising, the implications are less spectacular than an industry-wide breach, but potentially consequential. Publisher websites, advertiser landing pages and marketing technology applications all depend, to varying degrees, on the infrastructure now under scrutiny.
The question is not whether advertising has been hacked. There is currently no public evidence establishing widespread advertising-sector damage. It is how exposed the industry's interconnected operations could be when something so fundamental becomes vulnerable.
Related reports:
Who's really in control? How Meta, Google and Amazon are rewriting the rules of AI advtg
e4mXplains: Could advertising data become a national-security risk in India?
Meta's ad prices rise 14% globally in Q3, just 1% in APAC: The India equation
What actually happened?
Researchers identified serious weaknesses in PHP, a technology that helps websites process requests, retrieve information and deliver content.
PHP operates behind familiar content management systems including WordPress, Drupal and Joomla. WordPress alone powers a substantial proportion of the world's websites, including numerous digital publications.
The vulnerabilities created opportunities for attackers to interfere with affected websites, potentially access sensitive information or disrupt services. Not every website using PHP was necessarily vulnerable; actual exposure depends on how systems are configured and protected.
The weaknesses were discovered with AI assistance, adding an almost too-neat irony to an industry conversation already dominated by artificial intelligence.
The same technology being deployed to make businesses faster is also helping researchers discover problems in systems built long before the current AI boom.
The attackers, too, may have had AI on their side. While its role in these specific attempts remains unconfirmed, AI-assisted tools can accelerate the discovery and exploitation of vulnerabilities, potentially giving cybercriminals the same advantages of speed and scale that defenders are racing to harness.
AI truly is in everything.
From thousands to millions
According to figures shared by Cloudflare CEO Matthew Prince, attempted exploitation escalated dramatically around the public disclosure.
Thousands of attempts were observed beforehand. Within 45 minutes, the number had climbed into the tens of thousands. Within two hours, it reached hundreds of thousands. Soon afterwards, the total ran into the millions.
The escalation illustrates how quickly automated attacks can respond to newly disclosed weaknesses, leaving businesses comparatively little time to identify their exposure and implement fixes.
Crucially, millions of attempted attacks do not mean millions of successful breaches. Websites may be targeted repeatedly, and many attempts may fail.
As of October 23, the extent of successful intrusions, resulting financial losses and any specific impact on advertising infrastructure remains unclear.
Businesses and investigators are still establishing what, if anything, was compromised, which organisations were affected and whether attackers moved beyond attempted exploitation.
Some services have also been temporarily restricted as a precaution rather than because of confirmed breaches.
There is clear evidence of substantial attack activity and operational disruption. The final damage assessment is another matter.
Why should advertisers and publishers care?
For publishers, the immediate concern is website availability.
Advertising revenue depends on accessible pages, functioning ad placements and uninterrupted impressions. Compromised infrastructure, or even temporary downtime during emergency maintenance, could mean lost traffic, interrupted monetisation and additional costs.
A relatively brief outage during a major campaign can have commercial consequences, particularly for publishers dependent on programmatic advertising.
The second concern is data. Publishing and marketing systems may handle customer information, tracking integrations, analytics configurations and commercially sensitive material.
Successful exploitation could expose information or interfere with connected services, although there is no evidence that these vulnerabilities automatically compromise advertising cookies, bidding systems or audience databases.
For advertisers, exposure extends to campaign landing pages, ecommerce websites and conversion infrastructure.
A campaign may be running perfectly well, but if the website receiving its traffic becomes unavailable, advertising expenditure can continue generating clicks without producing the intended outcomes.
For adtech providers, risks depend on whether their own applications, dashboards or supporting services use affected systems. The vulnerabilities do not imply that the entire programmatic ecosystem is exposed.
Rather, the incident illustrates how failures in underlying web infrastructure can affect commercial systems built around it.
After all, even the most sophisticated AI-powered campaign optimisation is of limited use if the website at the other end of the click is unavailable.
Who is responsible when the chain breaks?
Digital advertising operates through numerous intermediaries, including publishers, advertisers, agencies, ad exchanges, technology vendors and hosting providers.
A single campaign can depend on several organisations with different security responsibilities. When something fails, accountability is not necessarily straightforward.
Ekta Rai, Advocate, Delhi High Court, says liability must be assessed according to the control and obligations of the parties involved.
"In my view, liability cannot be determined simply by identifying whose technology failed. We must also look at who controlled the risk, what security obligations each party had, and whether their failure to meet those obligations contributed to the incident," she explains.
Rai notes that publishers and advertisers may remain responsible for personal data handled on their behalf, while vendors can face separate contractual and legal obligations.
India's existing cybersecurity framework provides certain protections through the Information Technology Act and CERT-In's reporting directions, although these do not automatically address every breach, disruption or financial loss.
The Digital Personal Data Protection framework is expected to introduce more structured accountability when its core obligations take effect in May 2027.
"The real test, both now and under the DPDP regime, is whether accountability can be traced and enforced across that chain rather than getting lost between vendors," Rai adds.
What happens next?
Businesses are now identifying affected websites, installing updates and investigating suspicious activity. Publishers and advertisers must establish which systems are exposed, who maintains them and how quickly disrupted services can be restored.
The larger picture will emerge as organisations disclose findings and investigators determine whether attempted attacks resulted in successful intrusions.
It is possible the volume of attempted exploitation will prove considerably larger than the damage inflicted. Individual breaches may also emerge after the initial emergency has passed.
Either way, the incident illustrates an uncomfortable truth about the industry's technological ambitions.
While billions are being committed to AI, automation and increasingly sophisticated advertising infrastructure, much of the digital economy still depends on established software components whose security can be overlooked until something goes wrong.
And while AI helps researchers uncover weaknesses at unprecedented speed, organisations still need people to investigate, prioritise and repair them.
The PHP security scare has not yet been shown to have caused widespread advertising-industry damage. But it is a reminder that the future of digital advertising depends, in no small part, on maintaining the infrastructure already holding it together.
Preferably before the next earnings call.
Read more news about Digital Media, Internet Advertising, Marketing News, Television Media, Radio Media
For more updates, be socially connected with us onInstagram, LinkedIn, Twitter, Facebook, YouTube & Google News